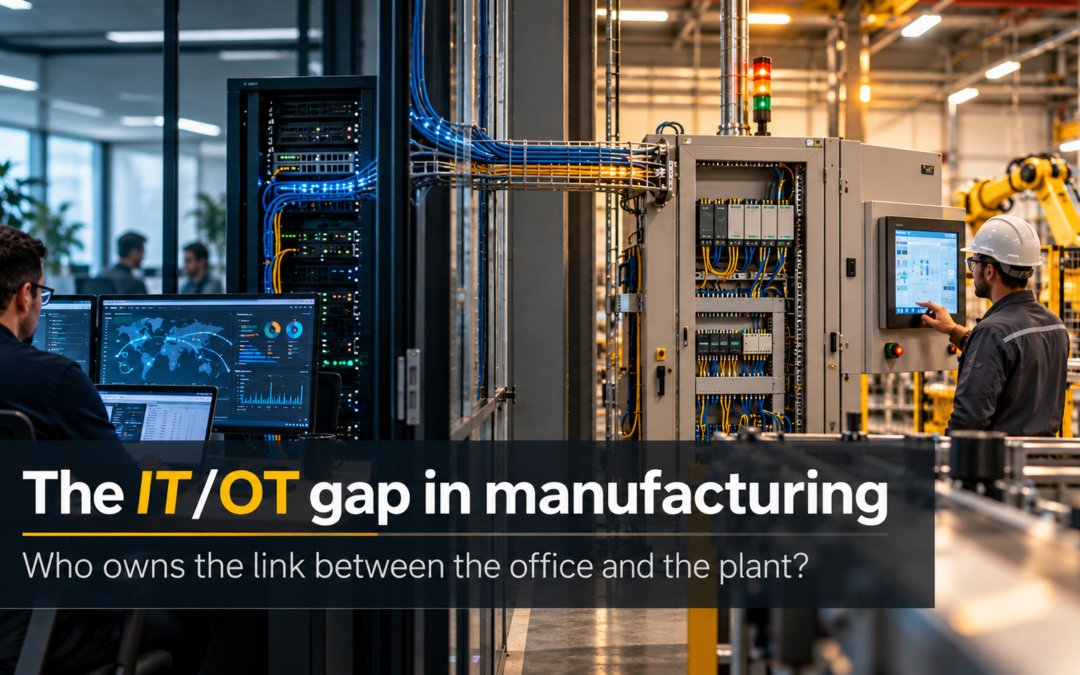
This article is for operations directors, engineering and plant managers at UK manufacturing sites, and for the business owners accountable for keeping production running. Most sites now connect production equipment to the business network for data and remote maintenance, but responsibility for those connections is rarely assigned.
Why the IT/OT gap matters now
The issue is becoming more pressing. Make UK reports that 30% of manufacturers experienced a cyber incident in the past 12 months, directly or through their supply chain. The EU Machinery Regulation 2023/1230, which replaces the Machinery Directive from 20 January 2027, treats cyber attack as reasonably foreseeable misuse of machinery, and the UK’s National Cyber Security Centre (NCSC) now asks operators to keep a definitive record of their operational technology (OT) and its connections.
What this article covers
This article covers:
- what we mean by the IT/OT gap, and why it exists
- how the gap typically appears on manufacturing sites
- what recent industry research shows
- three documented incidents and what they illustrate
- practical steps to close the gap
What we mean by the IT/OT gap
Information technology (IT) covers business systems such as ERP and office networks. Operational technology covers the systems that control the process: PLCs, HMIs, SCADA, drives and safety systems. IT security generally puts the confidentiality of data first. On the plant floor, safety and availability come first, and a routine IT action such as a reboot or an unscheduled update can stop a line or affect a safety function.
Control systems often run for 15 years or more, far longer than office IT, and the two report to different parts of the business. In practice, the IT provider is responsible for the office network, the automation contractor or in-house engineering team is responsible for the machines, and the connection between the two often has no named owner. That connection is what we refer to as the IT/OT gap.
How the gap appears on site
In my experience of industrial automation since 2006, the gap develops over years, as connections are added to meet specific needs. Each change is reasonable at the time, but few are designed, documented or reviewed as part of the whole system. Typical findings include:
- flat networks, where devices in the office can communicate directly with PLCs on the line
- remote access for machine builders or integrators that is still active years after commissioning, with no record of who uses it
- network drawings that reflect the original installation rather than the current site
- devices added for data collection that create an unplanned route between the plant and the internet
What the industry research shows
Make UK’s Cyber Security in Manufacturing report (August 2026) found that downtime and higher operating costs were the most common consequences of incidents. Only 51% of manufacturers had an incident response plan, and 45% had assigned senior leadership responsibility for cyber security. Research commissioned by ESET from 500 UK manufacturing decision-makers (April 2026) found that one in five had limited or no visibility of threats that could disrupt production.
Industrial cyber security specialist Dragos reported in its 2026 year in review that ransomware groups targeting industrial organisations affected around 3,300 organisations in 2025, with manufacturing accounting for more than two-thirds of victims. Organisations with comprehensive OT visibility contained ransomware incidents in an average of five days.
What documented incidents show
- Jaguar Land Rover (2025). JLR shut down its systems after a cyber incident in September 2025, and production at its UK plants stopped for around five weeks. Reporting describes an IT incident, yet production could not continue without those systems. The independent Cyber Monitoring Centre estimated the cost to the UK economy at around £1.9bn.
- Colonial Pipeline (2021). Attackers entered through a legacy VPN account no longer meant to be in use, and ransomware affected the business systems. The pipeline control systems were not reported as compromised, but operations were shut down for several days because the boundary between the two networks could not be confirmed.
- Triton (2017). At a petrochemical plant, attackers moved from the business network to the safety instrumented system, which brings the process to a safe state. Errors in the malware tripped the plant and led to its discovery. No one was harmed, but a network weakness had become a safety issue.
Closing the gap
The gap is closed through organisation and engineering discipline rather than additional products. The NCSC’s joint guidance on OT architecture (September 2025) and secure connectivity (January 2026) starts from the same point: you cannot apply effective controls to systems and connections you have not documented.
The DADA approach: Discover, Assess, Design & Deliver, and Assure
These steps work best in a set order, which is how we structure every engagement. We call it DADA: Discover, Assess, Design & Deliver, and Assure. Discover establishes what is actually on site, using evidence from the plant, the network and the documentation. Assess interprets that record to decide what matters most and what needs to change. Design & Deliver makes those changes, and Assure keeps the record and the controls current as the plant evolves. In our experience, the common mistake is to start at the third stage and buy a product before anyone has established what it needs to protect.
Five practical steps to close the IT/OT gap
We recommend five steps:
- Establish a single, current record. Cover assets and connections across the office and the plant, including protocols and network boundaries.
- Document and control remote access. List every route, who uses it and why. Remove those no longer needed and bring the rest through one managed, authenticated connection.
- Assign ownership of the boundary. Name a person or function responsible for the IT/OT connection, with authority to approve changes on either side.
- Agree decision rights in advance. Define who can isolate a line or network segment, under what conditions, and how engineering and IT coordinate during an incident.
- Maintain change control and drawings. Record PLC and network changes, and update drawings whenever the plant changes.
The first step is Discover; the second to fourth come from Assess and Design & Deliver; the fifth is Assure.
Why Hale Engineering works with Arlio
Hale Engineering’s expertise is the plant: control systems, automation and machine safety. On the IT side, we work with Arlio, a managed IT and cyber security provider, and we have already delivered client projects together.
Scott Gorman, Managing Director at Arlio, has written an article on the same subject from the IT perspective, and we recommend reading it alongside this one. It recognises that safety and availability come first in OT, and that understanding of operational constraints is the main reason we work with Arlio. Hale Engineering provides the engineering truth and Arlio provides the digital truth. Our joint Discover service reconciles the two into a single record, which is where closing the gap begins.
[link to Scott Gorman’s article: Arlio URL]
Conclusion
Industry research, documented incidents and government guidance point to the same conclusion: the main risk lies less in a shortage of security products than in undocumented connections with no clear owner. Manufacturers that keep a current record of their connections, control remote access and assign responsibility for the boundary will be better placed to prevent incidents, recover from them and meet the requirements that apply from January 2027. The starting point is Discover: a current, evidenced record of what is on site and how it connects.
Take the first step towards closing the IT/OT gap
To arrange OT Route-In Review / Discover: Asset & Connectivity Baseline for your site, please contact Hale Engineering, or follow us on LinkedIn for further articles on OT, control systems and machine safety.
Contact details:
Call: +44 20 8154 6102
Email: info@hale-eng.co.uk